MCP Security Best Practices: Check Your Own Server First
19 August 2026. Checked against MCP specification 2026-07-28.
Most MCP security best practice do not go far enough.
Hugging Face's AI breach needed AI to investigate it. The models refused.
Updated 21 August 2026: rewritten to cover all four evaluation disclosures. An earlier version said hosted models refuse forensic work
LiteLLM Security: Your AI Gateway Is a Secrets Manager. Benchmark It Like One
July 2026
An AI gateway is a secrets manager wearing a router's clothes. LiteLLM, the most widely adopted
Your AI Coding Assistant's Config Folder Is a Persistence Surface
Supply-chain malware started writing into the config files your coding agent reads on every run. Nothing in the usual toolchain is watching that surface.
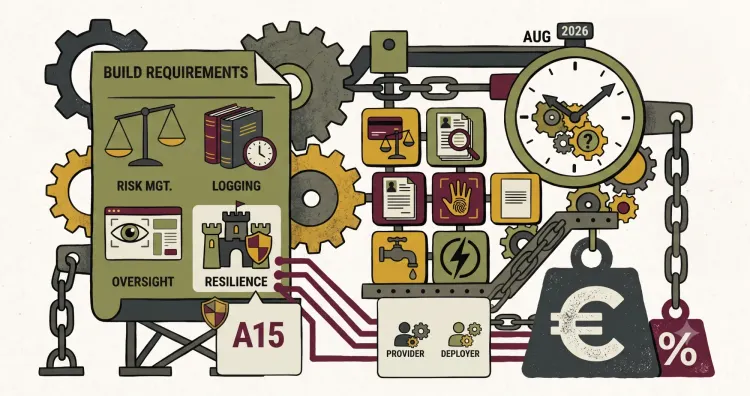
The EU AI Act Lands on Your Codebase, Not Just Your Legal Team
July 2026
The EU AI Act for developers and technical teams
The EU AI Act describes engineering work. Risk management,
The Agent Control Plane: Security's Third Sprawl
June 2026
Every major platform vendor is shipping an agent control plane this year, and most of them are selling
Claude Code Security Review: CodeGuard vs the Built-in Tools
June 2026
Claude Code can review your code for security flaws. Type /security-review and it scans your project for
Exposed AWS Credentials Are Used in Under 90 Seconds: Findings from AI Infrastructure Research
Exposed AWS credentials were used against live AWS APIs within 67 seconds of being harvested, faster than CloudTrail delivers the first event to a defender.
The Scanners Mapping AI Infrastructure Aren't After Your Model. They're After Your Credentials.
460 source IPs, 11,643 requests, 72 hours against exposed AI infrastructure. The operators that recognised it were cataloguing; the ones attacking were after credentials that sit on any exposed host.
Anthropic expected six months of lead on Claude Mythos. It got twenty days.
Last updated: 21 August 2026. What's changed: the export controls were lifted on 30 June and Fable 5